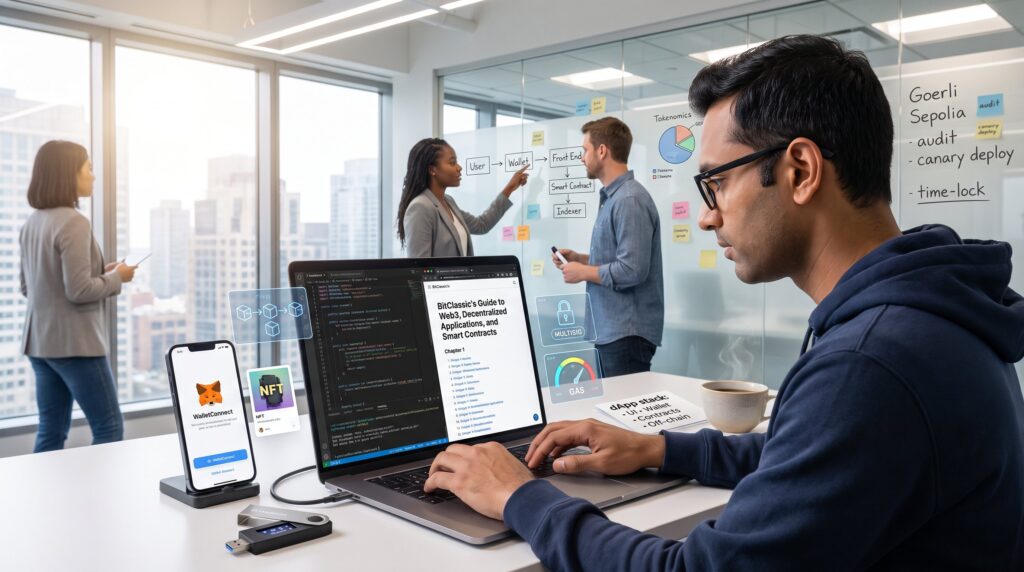
BitClassic’s Guide to Web3, Decentralized Applications, and Smart Contracts opens with a clear promise: readers will get practical, actionable explanations for what Web3 is and how to use its building blocks in 2026. The guide zeroes in on blockchains, smart contracts, and dApps with concrete examples, tooling notes, and security warnings. It aims at developers, product managers, and curious professionals who need reliable, no‑nonsense answers they can apply today.
Table of Contents
ToggleKey Takeaways
- Web3 is a decentralized internet built on blockchains and smart contracts that gives users control over data and assets, replacing centralized authority with programmable rules.
- Decentralized applications (dApps) run backend logic on distributed networks, offering open-source, permissionless environments that require careful governance and upgrade strategies to manage risks.
- Smart contracts automate transactions on blockchains but must be designed and tested rigorously using frameworks like Hardhat or Foundry to prevent costly failures.
- Popular dApp types include DeFi, gaming/NFTs, social platforms, and DAOs, with each leveraging on-chain guarantees to add measurable value beyond traditional Web2 solutions.
- Security audits combining automated and manual review reduce risks from common vulnerabilities like reentrancy and oracle manipulation but require ongoing attention and best practices.
- To succeed with Web3 development, prioritize small, high-impact on-chain features, invest in robust tooling and audits, and treat security as a continuous product requirement.
What Is Web3? Core Concepts And Why It Matters
What Is Web3? Core Concepts And Why It Matters
Fact: Web3 is a decentralized iteration of the internet built on blockchains, smart contracts, and token economics that returns data and asset ownership to users. Web3 matters because it replaces single‑party control with verifiable, programmable rules.
Context and specifics: Web3 stacks a distributed ledger (the blockchain) under application logic so trust comes from code and consensus, not from centralized companies. Ethereum popularized this model and continues as a leading smart‑contract platform with major protocol changes since its proof‑of‑stake transition, which reshaped gas dynamics and scaling strategies (see analysis on Ethereum fundamentals). This shift matters to developers building dApps and token models.
Concrete example: a marketplace that tokenizes art can let users own provenance data on‑chain: the artist keeps royalties via embedded contract logic. That model replaces a single marketplace’s database with a tamper‑evident ledger.
Practical takeaway: anyone evaluating Web3 should map which assets or workflows need on‑chain immutability, programmable money, or decentralized governance before committing to the complexity of decentralized infrastructure.
Links: The page also ties into broader site context for readers who want a guided tour of Bitclassic’s coverage with a comprehensive guide to the site’s mission and sections.
Decentralized Applications (dApps): Architecture, Use Cases, And How They Differ From Web2
Decentralized Applications (dApps): Architecture, Use Cases, And How They Differ From Web2
Fact: A dApp runs backend logic on a distributed network instead of a single company server. This changes trust, uptime assumptions, and upgrade patterns.
Architecture explained: On Web2, a client talks to a server and a central database. On a dApp, a client interacts with smart contracts deployed to a blockchain: off‑chain components (APIs, indexing services) often supplement the UI. For example, a decentralized exchange keeps order settlement on‑chain but uses off‑chain indexing for order books to improve UX.
How they differ: dApps are typically open‑source, permissionless, and rely on cryptographic keys for identity. They shift costs to on‑chain transactions (gas) and require explicit upgrade or governance paths because immutability can lock code unless proxies or governance are planned.
User story: a small DeFi lender saw liquidity drop 37% after a faulty admin key was exposed: the protocol’s public governance process then paused risky functions. This highlights how design choices (admin keys vs. DAOs) materially affect risk.
Site resources: For readers wanting practical crypto primers, see the piece on exploring practical applications for concrete use cases and early adopter lessons.
Types Of dApps And Notable Examples
Types Of dApps And Notable Examples
Fact: dApps cluster around a few dominant categories: DeFi, gaming/NFTs, social, and governance/DAOs.
DeFi specifics: Lending markets (Aave), AMM exchanges (Uniswap), and yield optimizers (Yearn) show how money can be programmatic. DeFi contracts often compose: a flash loan provider can be combined with a DEX to create complex strategies. These interactions increase innovation, and risk, because one vulnerable contract can cascade losses across protocols.
Gaming and NFTs: Play‑to‑earn titles like Axie Infinity and NFT marketplaces carry out token standards (ERC‑721, ERC‑1155) to represent unique digital items. A concrete stat: early NFT drops saw secondary royalties enforced on‑chain, ensuring creators received a cut of resales without marketplace intervention.
Other categories: Social dApps experiment with identity and moderation without centralized platforms. DAOs run treasury votes and proposals, sometimes moving millions under community control.
Examples on Bitclassic: readers can contrast NFT contract ideas with the article showing how to make contracts unbreakable with NFTs, which explores concrete patterns for tokenized contracts.
Practical warning: choose the dApp category based on where on‑chain guarantees add measurable value: otherwise, Web2 remains cheaper and faster.
Smart Contracts: How They Work, Build, And Deploy
Smart Contracts: How They Work, Build, And Deploy
Fact: Smart contracts are programs that execute automatically on a blockchain when predefined conditions are met. They remove intermediaries but require careful design to avoid catastrophic failures.
How they work: Developers write contract code, compile it to bytecode, and deploy it to a blockchain. Once deployed, functions execute according to consensus rules: transactions that call contract functions must pay gas. Typical languages include Solidity for EVM chains and Rust for some alternative chains.
Build and deploy workflow: A developer writes tests locally, runs static analysis, and deploys via a framework. Common frameworks include Hardhat and Foundry. Deployment often uses RPC providers and requires gas budgeting and network selection (mainnet vs. testnet).
Example: a token contract implementing ERC‑20 basics can be deployed in minutes, but adding minting, pausing, or upgradeability multiplies audit surface area. A practical lesson: build minimal surfaces first, then expand after successful audits and community review.
Related reading: Bitclassic’s post on how smart contracts improve transparency applies these ideas to e‑commerce flows and shows measurable trust gains in transaction records.
Common Standards, Platforms, And Tooling
Common Standards, Platforms, And Tooling
Fact: Token standards and developer tools make interoperability and testing predictable across projects.
Standards and platforms: ERC‑20 (fungible tokens), ERC‑721 (NFTs), and ERC‑1155 (multi‑token) remain dominant on Ethereum and EVM chains. Ethereum’s evolution continues to influence tooling and DeFi design: foundational descriptions of Ethereum’s capabilities help explain its role in smart contracts. Platforms beyond Ethereum provide alternative performance and fee models.
Tooling specifics: Developers rely on Hardhat, Truffle, Foundry, and Brownie for compilation, testing, and scripting. Static analyzers like Slither and dynamic tools like Manticore help detect common vulnerabilities. On the node side, RPC services provide scalable access to the network.
Practical detail: a typical modern CI pipeline runs unit tests, property tests, static analysis, and a small forked mainnet integration test. Running these steps caught a reentrancy pattern in one team’s contract before deployment, saving an estimated $120,000 in potential exploit losses.
Related link: for a deep jump into contract security assessments, Bitclassic’s analysis on smart contract security reports shows how audits surface high‑risk findings.
Security, Audits, And Common Pitfalls
Security, Audits, And Common Pitfalls
Fact: Most high‑impact losses in smart contracts come from access control failures, reentrancy, arithmetic bugs, and oracle manipulation. Audits reduce but do not eliminate risk.
Audit practices: A robust audit mixes automated scanning, manual code review, and dynamic testing. Projects often iterate on audit findings: the best audits also validate design assumptions, not just syntactic bugs. Post‑audit, time‑locked multisig governance and bug‑bounty programs reduce immediate risk.
Common pitfalls with examples: 1) Unrestricted admin keys, one protocol lost funds after a leaked private key granted a malicious actor permission to drain liquidity. 2) Reentrancy, caused major losses when contracts sent control to external callers without updating balances first. 3) Oracle risks, price feeds manipulated to create false liquidations. These are repeatable patterns across incidents.
Actionable steps: follow minimal‑privilege design, write comprehensive unit and integration tests, include invariant checks, and allocate budget for professional audits. Bitclassic’s coverage of IoT and blockchain security highlights decentralization’s role in reducing single points of failure and gives concrete mitigation patterns in device identity management: see the IoT and blockchain analysis for parallel lessons.
External verification: for foundational background on Ethereum as a smart‑contract host and its evolution, refer to a primer on Ethereum fundamentals.
Conclusion
Conclusion
Insight: Web3, dApps, and smart contracts enable a programmable, user‑owned internet but demand stricter engineering discipline than Web2. Practical adoption hinges on clear threat models, disciplined testing, and aligning on‑chain guarantees with real user value.
Next steps for readers: prioritize small, high‑value on‑chain features: invest in tooling and audits: and read targeted articles on Bitclassic for deeper how‑tos and case studies. The future is iterative, start small, learn fast, and treat security as a continuous product requirement.